
OPCNet Broker® DA HDA AE is an all-in-one OPC tunneling product
- Eliminates DCOM configuration headaches.
- Provides secure and encrypted communications.
- Supports OPC Data Access, Historical Data Access, and Alarms and Events.
- Works seamlessly across firewalls and segmented networks.
- Enables reliable remote OPC connectivity in minutes, not hours
OPC Support & Services
OPC DA
Secure tunneling for OPC DA servers.
- Full compliance with the OPC DA specification (2.05a and 3.0)
- Address-space browsing and tag translation from the source server
- Read, write, and subscriptions with full value, quality, and timestamp fidelity
OPC HDA
Historical data tunneling
- Full compliance with the OPC HDA specification
- Support for both raw and aggregated (processed) data
- Standard HDA aggregates (average, min/max, interpolative, time-average, count, etc.)
- Raw, processed, and read-at-time queries with end-to-end timestamp/quality fidelity
OPC AE
Event and alarm tunneling.
- Full compliance with the OPC AE specification
- Support of alarm acknowledgement across the tunnel
- Condition, tracking, and simple event handling with area/source browsing
- Event filtering and condition-state refresh for a complete, accurate alarm picture
How ONB® compares to native DCOM communications
| Capability | DCOM | ONB: OPCNet Broker |
|---|---|---|
| Configuration | Manual DCOM configuration on every machine: security settings, user permissions, user accounts sharing | Deployed and configured in a few clicks. No DCOM configuration required |
| Firewall & Port Handling | Requires opening a wide, often dynamic range of ports, multiplying security exposure Requires opening a well known TCP port number | Single port open in the firewall, port number configurable Tracks client/server communication through a single TCP port, minimizing security holes |
| NAT, DMZ & Proxy Traversal | Not designed for NAT traversal; typically breaks across firewalls, DMZs and proxies | Navigates NAT, DMZ, firewalls and proxies natively |
| Security & Compliance | Relies on the native Windows security model. No built-in encryption | IEC 62443-aligned; built-in data encryption and user authentication |
| Call Timeout Handling | Fixed, mandatory 6-minute call timeout after a communication failure | Configurable call timeout parameters, so activities restart far faster after a glitch |
| Network Efficiency | No native data compression | Built-in data compression, reducing bandwidth costs and network strain |
| Recovery After Disruption | Manual intervention typically required after a network glitch | Automatic OPC reconnection and data recovery after communication glitches |
| Redundancy | No native redundancy management; requires custom engineering | Built-in servers redundancy management (active-active, active-passive) |
| Cross-Domain Connectivity | Difficult across domains without established trust relationships | Connects OPC components across different domains, LAN and WAN |
| Ongoing Maintenance | Prone to breaking after Windows/security updates; requires repeated DCOM tuning | Easy to deploy and maintain, via a graphical user interface |
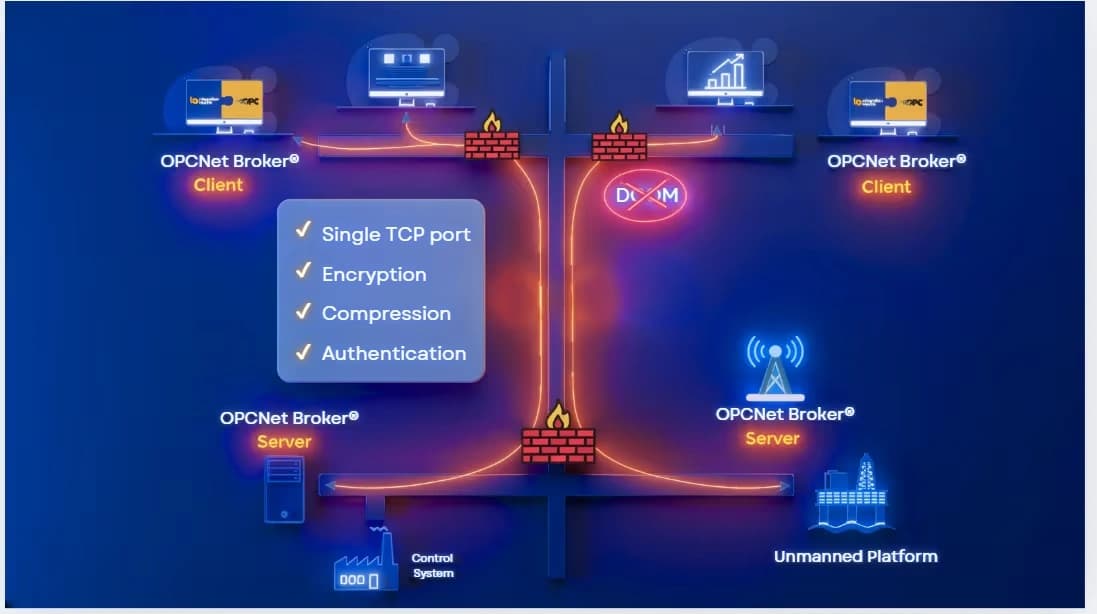
It replaces DCOM with a reliable TCP-based communication layer that operates through a single configurable port, simplifying connectivity, and improving resilience.
Yes, OPCNet Broker is completely transparent to existing OPC applications. It acts as a proxy, allowing any OPC DA, HDA, or AE client to connect to remote servers without requiring application modifications or updates.
OPCNet Broker ensures communication integrity through data encryption, user authentication, application whitelisting, and the Tag Security add-on, while aligning with ISA/IEC 62443 industrial cybersecurity principles.
OPCNet Broker supports communication across firewalls, NAT devices, different domains, VPNs, and DMZ configurations. It only requires a single TCP port to be opened, simplifying firewall configuration.
OPCNet Broker is optimized for minimal latency and high throughput, making it suitable for real-time industrial applications.
Most installations can be completed in under 30 minutes using the configuration wizard and the graphical configuration interface. No complex DCOM settings or registry modifications are required.
ONB (OPCNet Broker®) tunnels OPC DA, HDA and AE data without DCOM's manual configuration, fixed port ranges and 6-minute timeout, adding built-in encryption, authentication, compression and automatic reconnection. ONB establishes secure OPC communications through a single TCP port.
OPCNet Broker® DA HDA AE Resources
Product Datasheet
Comprehensive technical specifications and features overview
Related Blogs
See the OPC product in action with real-world examples
User Guide
Step-by-step installation and configuration guide
Whitepaper
Industrial Network Security with OPC Tunneling